Before the what, the how
We work with seven principles, refined over real projects. They explain why our proposals look very little like a standard report.
The hard part of this work is rarely knowing what needs to be done. It is understanding why, in that organisation, it has not been done yet, without jumping to hasty conclusions.
Behind a control that is not applied there is usually a reasonable operational reason. Finding it is what separates a recommendation that takes root from one that gets filed away. These seven principles are, in practice, how we go looking for it.
We listen before we intervene
The first conversations are not for selling an approach. They are for understanding yours.
Before giving an opinion we need to hear from those who decide and those who carry it out, who rarely describe the same reality. The head of security explains the basis of the programme; the night shift explains how it is applied. Both versions are true, and the distance between them is precisely the information we need.
That is why we start with short meetings, reading what already exists and time spent in the operation. A proposal written without setting foot on the site shows (and does not survive the first hard question).
We understand the context before proposing
The same measure can be right in one organisation and a hindrance in another.
Context is the sector, the size, the collective agreement, the culture, the moment the business is in and who really has the power to decide. There are correct recommendations that do not fit because they arrived in the wrong quarter, or because they required a role that does not exist in that structure.
We also ask about what was tried before and did not work. It is usually the most useful piece of information in the whole project, and it almost never appears in any document.
Four questions before we propose anything
Security of what, for whom, against what, and in which situation?
The question comes from Giovanni Manunta and we have yet to find a better one. Until it can be answered in full, there is no defined problem; perhaps there is only a label.
Defining the asset properly shapes everything that follows, because the asset is almost never the object itself: the pallet matters because of the commercial flow that depends on it, and protecting a person means protecting their ability to live their life and do their job.
We build on what already works
You very rarely have to start from scratch, and it is almost never a good idea.
In most organisations there is already sound judgement, experienced people and reasonable procedures. The job is not to replace all that. It is to organise it, complete what is missing and remove whatever survives on inertia alone.
That is why we are wary of off-the-shelf solutions. They age badly, because the context that justified them moves on and expires. What sustains a measure is the reasoning behind the decision, not the template it was copied from.
It also means giving credit for previous work, by name, in front of senior management. A project that begins by discrediting the internal team loses the very people who will have to sustain it afterwards.
We look for measures that hold up day to day
A measure the operation works around does not protect, however well it is written.
Before recommending anything we ask ourselves who will do it next month, whether they have the time to do it and what happens the day that person is on holiday. If the answer depends on the goodwill of one particular individual, the measure is incomplete.
We prefer a little that is well embedded to a great deal of theory on paper. It is less impressive in a presentation, and it stands up far better to the passing of time and to audits.
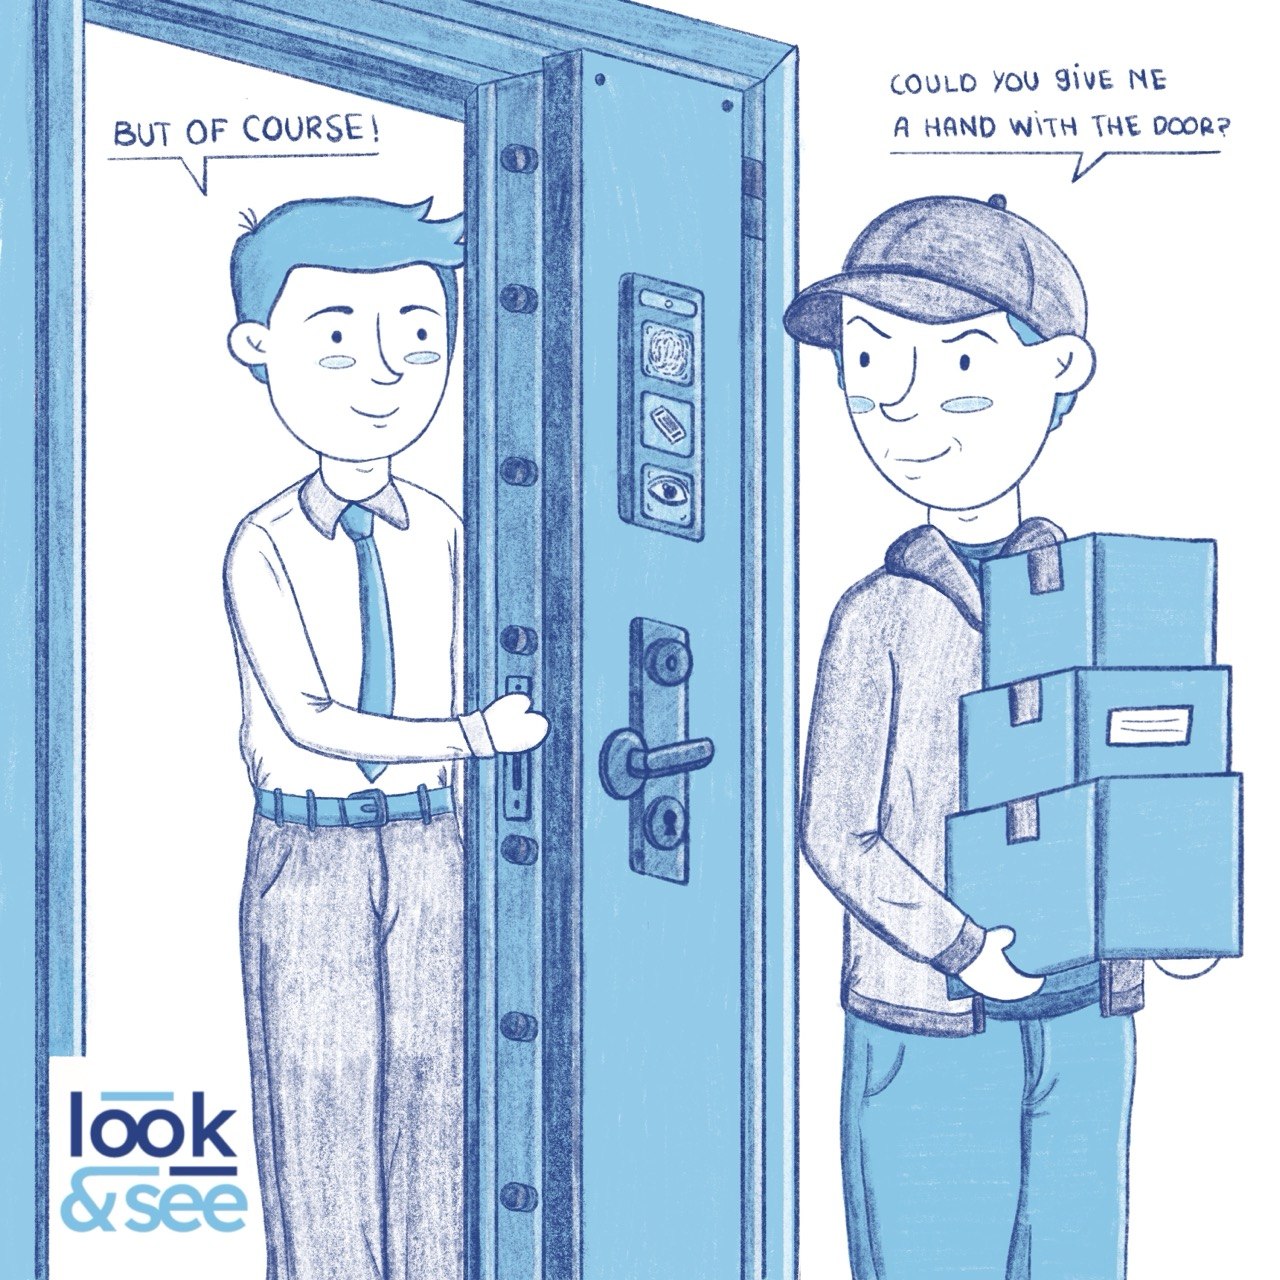
Companies invest in the physical protection of their premises. Do not let good manners undermine access control.
We watch for the warning signs
Many incidents give warning before they happen.
Gavin de Becker teaches that violence almost never arrives unannounced and that the early signals can be learnt. People in public-facing roles can notice them before the incident. A good protection programme, with the training to go with it, gives them a language to name those signals, a channel to report them and a response that does not leave them on their own.
Teams that learn to read those signals can go as far as preventing it. That is the difference between managing an assault and avoiding one.
Security protects people, plans and objectives
A programme that slows the business down ends up switched off. One that forgets people ends up costing far more.
Security is not an end in itself. It exists so that people can work without being exposed and so that the organisation achieves what it set out to do. Forget the first part and incidents appear; forget the second and the permanent exception appears.
That shapes how we write a procedure, how an investigative interview is prepared and how an overnight truck stop in the supply chain is planned: there is always a person on the other side of the decision. We see it every day in retail, in warehouses and on the road.
We do not replace an organisation's internal knowledge. We bring an independent perspective built on real experience, and we put it to work alongside your team's.
A method note
If this way of working suits you
Tell us where you are and what has already been tried. With that we can tell you whether we have something useful to add, or whether the problem is better solved from within.